


Black Friday 2026 is on Friday, November 27, with Cyber Monday following on November 30. For WordPress site owners it’s the one week a year when the plugins and services…
Table of contents
In a 2024 ETH Zurich study, a YOLO-based model solved 100% of reCAPTCHAv2 image challenges, where earlier work had topped out at 68 to 71% (Plesner, Vontobel and Wattenhofer, COMPSAC 2024). The puzzle no longer tells people and scripts apart, which is most of the reason site owners go looking for something else.
CAPTCHA alternatives verify a visitor is human without a visual or audio puzzle. They rely on passive signals, a computational task, a hidden form field or a cryptographic token. Cloudflare Turnstile, proof-of-work widgets such as ALTCHA and Friendly Captcha, honeypot fields and Privacy Pass tokens all fit.
Most people switching want spam and fake sign-ups gone from forms and credential stuffing gone from logins, and they don’t want to add friction to get there. Each option gets measured against reCAPTCHA on how hard it is to bypass, how it handles privacy and accessibility, and what it costs.
What Are the Main CAPTCHA Alternatives?
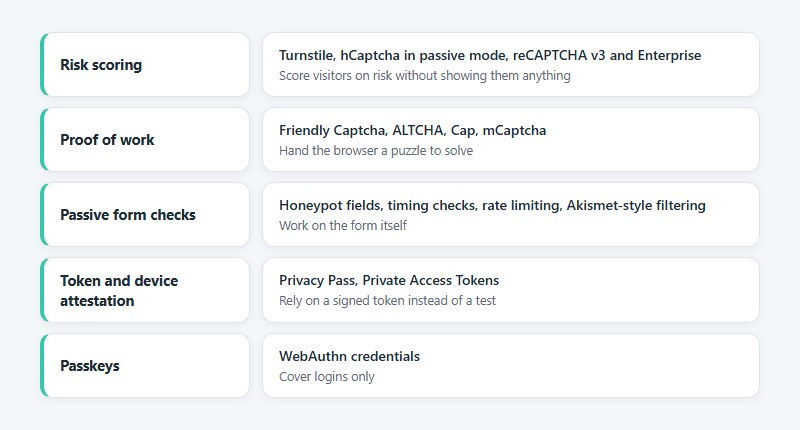
In production today, nearly everything lands in one of these buckets.
- Turnstile, hCaptcha in passive mode, and reCAPTCHA v3 and Enterprise score visitors on risk without showing them anything.
- Friendly Captcha, ALTCHA, Cap and mCaptcha hand the browser a proof-of-work puzzle to solve.
- Honeypot fields, timing checks, rate limiting and Akismet-style filtering work passively on the form itself.
- Privacy Pass and Apple’s Private Access Tokens rely on token and device attestation.
- Passkeys (WebAuthn credentials) cover logins only.
Friction runs from none at all for proof-of-work, honeypots and tokens up to an occasional checkbox or challenge with Turnstile in managed mode or hCaptcha Pro. If a typical visitor has to select, drag or type something, the method has crept back into CAPTCHA territory.
hCaptcha’s free plan doesn’t make the list. Its documentation says most users on that tier are shown a challenge, so it is a CAPTCHA with a different privacy pitch.
Full bot management platforms such as DataDome and Cloudflare Bot Management sit a step beyond all this. They are built for high-risk flows like checkout and login abuse.
Why Image CAPTCHAs Stopped Working Against Bots
Bots now match or beat people at image and text CAPTCHAs. Two peer-reviewed studies, one from 2023 and one from 2024, put numbers on it.
The ETH Zurich team’s YOLO-based model solved 100% of reCAPTCHAv2 image challenges, against 68 to 71% in earlier work (Plesner, Vontobel and Wattenhofer, ETH Zurich, 2024). They also found no significant difference between how many challenges humans and bots had to solve in reCAPTCHAv2.
The USENIX study went at it from the human side. It had 1,400 participants solve 14,000 unmodified, real-world CAPTCHAs, and people managed only 50 to 84% accuracy on distorted text while bots landed just under 100% (Searles et al., USENIX Security, 2023). Bots needed under a second on distorted text. People needed up to 15 seconds.
On reCAPTCHA click tasks, human accuracy was 71 to 85%, versus 100% for the bot result the paper cites from earlier work. Worth knowing that the bot numbers come from published attacks, so the comparison sets fresh human measurements against older attack results.
The ETH paper has a detail that gets quoted less. reCAPTCHAv2 leans heavily on cookie and browser history data, and the researchers’ bot stayed undetected using a VPN plus realistic mouse movements and browser data.
That cuts both ways. Behavior-based scoring is harder to beat than a grid of traffic lights, but a bot that looks like a person with a history still gets through.
Puzzle difficulty stopped being the signal. Defense moved to behavior, device environment and cost per request, and that is where the alternatives compete.
How Do Turnstile, hCaptcha and reCAPTCHA Compare?
For most sites that want a free, mostly invisible check, Turnstile is the one I’d start with. hCaptcha only pays off on a paid plan. reCAPTCHA makes the most sense if you already work inside Google Cloud.
| Service | Pros | Cons |
|---|---|---|
| Cloudflare Turnstile | Free plan, no image or text puzzles, three widget modes | Widget limits on the free plan; managed mode can still show a checkbox |
| hCaptcha | Common reCAPTCHA replacement; 99.9% passive mode on Pro | Free plan shows a challenge to most visitors |
| reCAPTCHA v3 and Enterprise | v3 never interrupts the visitor (Enterprise can add a verification step); per-action scores | Billed through Google Cloud; thresholds need tuning |
Cloudflare Turnstile
Cloudflare moved its own challenges from reCAPTCHA to hCaptcha in 2020 and built Turnstile after that. By its own measurements, time spent in a challenge fell from an average of 32 seconds to about one second for its non-interactive challenges (Cloudflare launch announcement, 2022).
As of November 2026, the documentation describes managed, non-interactive and invisible modes.
Managed mode lets Cloudflare decide per visitor, and a checkbox only appears when signals look risky. There are no images or text to decipher either way. Non-interactive mode shows a widget with a loading spinner and never asks the visitor to do anything. Invisible mode has no widget at all, and the browser challenge runs silently.
Every pass returns a token, and the server has to validate it through the Siteverify API before it accepts the login or form submission.
hCaptcha
The free plan is still a CAPTCHA.
As of November 2026, hCaptcha’s documentation describes the free tier as a classic experience in which most users are shown a challenge. The 99.9% passive mode, which scores visitors on thousands of factors and challenges only some of them, starts at Pro. Pro also adds custom themes and analytics, and risk scores sit in Enterprise.
If friction is the reason you’re leaving reCAPTCHA, the free hCaptcha tier won’t fix it.
reCAPTCHA v3 and Enterprise
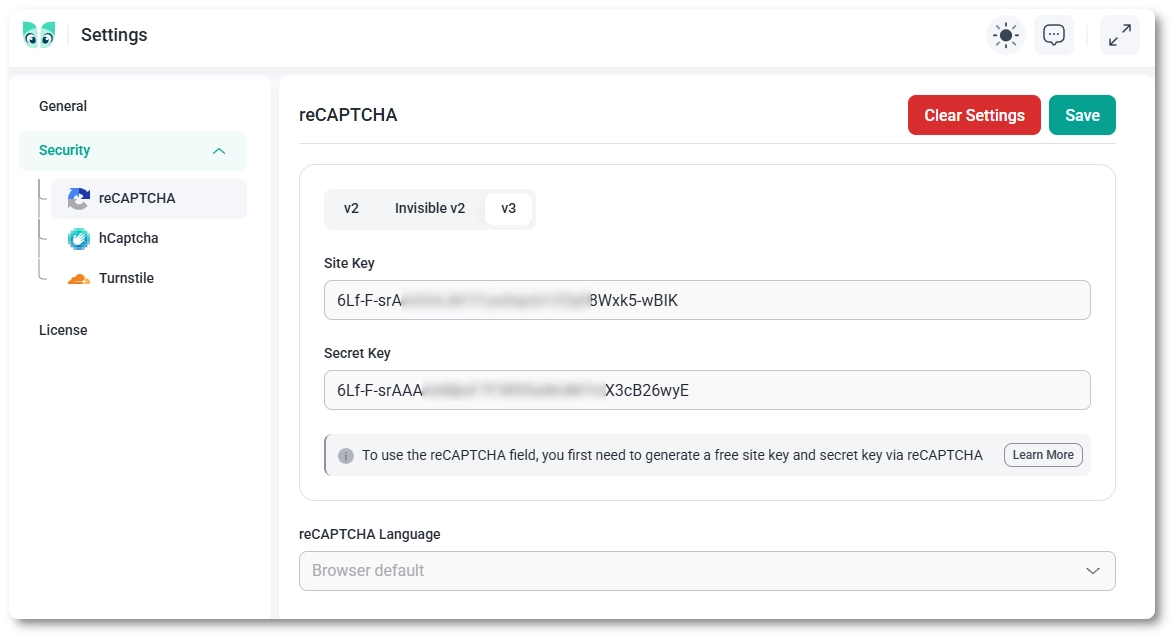
reCAPTCHA v3 returns a number from 0.0 to 1.0 for every request, where 1.0 is very likely a good interaction and 0.0 very likely a bot (Google reCAPTCHA documentation).
Google suggests starting the threshold at 0.5 and adjusting per action after watching real traffic in the admin console. It also recommends acting in the background instead of blocking outright, for example requiring two-factor authentication or email verification on low-scoring logins.
Enterprise adds advanced reason codes in assessments, available after a security review on request. Its keys live in Google Cloud projects, where billing is handled, and reCAPTCHA now sits under Google Cloud Fraud Defense.
WordPress sites usually meet reCAPTCHA through a form plugin, and setting up reCAPTCHA on a WordPress contact form comes down to pasting a site key and a secret key.
Privacy Pass and Private Access Tokens
Apple introduced Private Access Tokens at WWDC 2022 for iOS 16 and macOS Ventura, with Cloudflare and Fastly as the first token issuers (Apple Developer, 2022).
Apple attests that the device is in good standing and an issuer signs a token. The website redeems it and never learns who the visitor is.
Underneath sits Privacy Pass, an IETF standard (RFC 9576). Cloudflare’s documentation says it dropped legacy Privacy Pass v1 tokens as an alternative to its challenges in September 2023 and removed the public API in March 2024.
Tokens only help visitors whose device and browser support them, and Turnstile treats them as one signal among several, not as a replacement for the widget.
Proof-of-Work CAPTCHA Alternatives
Nobody sees a proof-of-work widget do its job. The browser gets a cryptographic puzzle, solves it, and the server verifies the answer, so a bot pays in compute for every request it sends.
ALTCHA’s documentation calls the design asymmetric, meaning it is cheap for the server to check and costly to solve at scale. No cookies or cross-site tracking are involved, and no personal data is needed to make the call.
- Friendly Captcha is paid and has an EU-only hosting offer. Its signals compute a risk score, and a higher score raises the puzzle difficulty.
- ALTCHA is an open-source widget with server libraries you host yourself. The paid Cloud and Sentinel layers add risk-based escalation to an accessible interactive check.
- Cap is open source (Apache 2.0) proof-of-work with browser-instrumentation challenges and a verification endpoint shaped like reCAPTCHA’s siteverify.
- mCaptcha is a self-hosted proof-of-work service for teams that want to run the whole stack.
Proof-of-work taxes requests. It doesn’t prove a human is present.
A bot can compute the hash too, which is why ALTCHA frames the defense as cost at scale. Raise the difficulty and visitors on old phones feel it. Keep it low and a well-funded attacker barely notices.
Friendly Captcha says solve times vary wildly across devices with a single hard puzzle, so it splits the work into several smaller ones. ALTCHA also supports memory-bound algorithms (Argon2 and Scrypt) meant to resist GPU and ASIC acceleration.
Read vendor claims carefully. Friendly Captcha says its approach produces zero false positives by design, which is a vendor statement and not an audited figure.
The license reads differently depending on where you look. Friendly Captcha markets its widget as open source, yet the friendly-pow package on npm carries the Friendly Captcha License and is labeled source-available.
Self-hosting swaps a monthly fee for patching duty. Fewer vendors in the loop, more upkeep on your side.
Do Honeypots, Timing Checks and Rate Limiting Stop Form Spam?
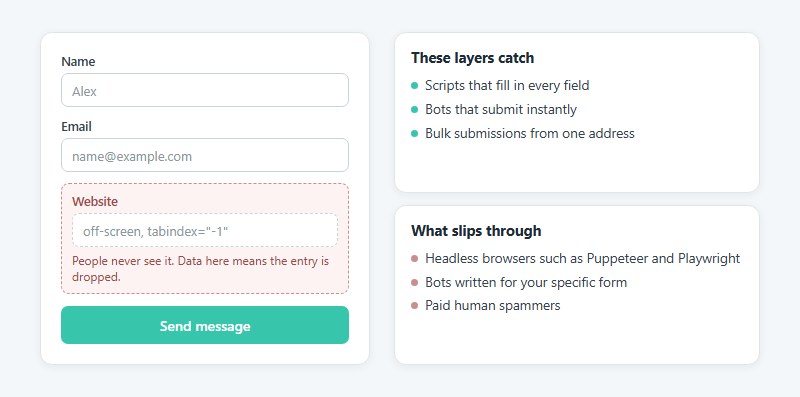
Mostly, as long as the spam is low effort. Headless browsers and paid human spammers walk right past them. For a contact form with little abuse incentive, that is often enough.
The honeypot is the simplest layer. A hidden input that people never see gets filled in by naive scripts, and any submission with data in it gets dropped. The mechanics of how a honeypot traps bots take a few lines of CSS and one server-side check.
- Pick a believable field name such as “website”. Bots skip fields called “honeypot” or “trap”.
- Move the field off-screen and add tabindex=”-1″ and aria-hidden so keyboard and screen reader users never land in it.
- Return a normal success response to the bot so it doesn’t learn it was caught.
- Keep your logs free of personal data.
For timing checks, store a signed timestamp when the form loads and reject submissions that come back too fast. OpenReplay’s guide puts the cutoff under 3 seconds, while one tutorial on phpcaptcha.org uses 2 seconds because browser autofill can beat typing. Test the threshold on your own form.
Sign the timestamp with an HMAC on the server. A bot cannot forge an old one.
Rate limiting caps submissions per IP address or session. Cloudflare’s documentation notes that visitors behind VPNs and Tor tend to have poorer IP reputations, and so do some shared networks, so a strict per-IP cap will catch real people there.
Akismet, built by Automattic, scores each submission on the server with machine learning. It covers WordPress comments and plugs into form plugins like Contact Form 7 and Gravity Forms, and into Jetpack Forms as well.
Expect an occasional false positive, mostly when a legitimate user’s text was already flagged on another site. Check the spam queue for the first few weeks.
These layers catch scripts that fill in every field and bots that submit instantly. Bulk submissions from one address run into the rate limit. A no-duplicates option on a field can also stop the same value being submitted twice.
What slips through is headless browsers such as Puppeteer and Playwright, which read the CSS and can spot hidden fields. Bots written for your specific form learn the field name and the timing. Paid human spammers fill forms by hand and walk past honeypots too, according to OpenReplay’s guide.
Gravity Forms’ reCAPTCHA add-on shows the layering in practice. Its documentation notes that the add-on skips its score check when a honeypot or another filter already flagged the entry as spam, so reCAPTCHA was never asked.
If these free layers still leak, the wider set of tactics for form spam prevention covers what to add next.
Which CAPTCHA Alternatives Meet WCAG 2.2 and GDPR Requirements?
Invisible and passive checks sidestep the WCAG 2.2 problem because they ask for no cognitive test. GDPR exposure depends on cookies and on where visitor data ends up. Self-hosted proof-of-work and passive checks carry the least risk, and reCAPTCHA is the most contested.
WCAG 2.2 and authentication
SC 3.3.8 Accessible Authentication (Minimum) covers logging in to an existing account, according to the W3C’s Understanding document. A contact form involves no authentication, so the criterion doesn’t apply to it.
Several vendor guides say every puzzle CAPTCHA fails WCAG 2.2. The W3C text is narrower. A login that uses a cognitive function test still passes at Level AA when it offers one of the following.
- Another login method with no cognitive test, which has to pass the criterion itself (TPGi).
- A mechanism that helps, such as password manager autofill or copy and paste.
- A test that only asks the user to recognize objects.
- Identification of non-text content the user supplied.
With multi-factor authentication, every step has to comply.
An image CAPTCHA that asks users to pick crosswalks therefore passes at AA through the object recognition exception. The W3C still advises avoiding it, and it fails Level AAA under SC 3.3.9, which drops the object recognition and personal content exceptions.
An invisible check sidesteps the question. TPGi’s testing guidance marks the criterion not applicable when authentication uses no cognitive function test.
The CAPTCHA is one barrier among several. Labels and focus order decide a good part of the rest, along with how error messages read, and a checklist of form accessibility best practices covers them.
Passkeys and WebAuthn
Passkeys are FIDO credentials built on WebAuthn, the W3C browser API that creates and uses them. Each site gets its own key pair. The private key stays on the device and the server only stores the public key.
Nothing is memorized or solved, so a passkey login never raises the 3.3.8 question. The FIDO Alliance describes passkeys as phishing-resistant replacements for passwords.
The catch is scope. A passkey belongs to an existing account, so it’s no help on a newsletter box or a comment field. First-time sign-ups are out too.
Cookies, fingerprinting and GDPR
Google says reCAPTCHA Enterprise collects device and application data only to provide and improve the service and for general security, and not for personalized advertising (Google Cloud blog).
Regulators read it differently. France’s CNIL has flagged that reCAPTCHA cookies need consent when they mix security with other purposes (Bird & Bird, 2025), and Austria’s Federal Administrative Court ruled on 13 September 2024 that reCAPTCHA is only permissible with express consent, according to law-firm summaries of the decision.
The CNIL’s decision on e-scooter operator Cityscoot also addressed its use of reCAPTCHA on account creation and login, and on password recovery (National Law Review).
Both positions stand. Google describes what the data is used for, and regulators decide whether it is strictly necessary. Whether the widget loads before or after consent is up to the site operator.
ALTCHA is self-hosted, so there is no outside processor to document. Friendly Captcha’s EU-only hosting offer keeps visitor data inside the EU. Cloudflare calls Turnstile privacy-preserving, but challenge signals still pass through Cloudflare, so list it as a processor. Passive checks involve no third party at all, though stored IP addresses can count as personal data under the CJEU’s Breyer ruling.
The cookie banner and privacy notice need to match what the page actually loads. A guide on how to create GDPR-compliant forms covers consent wording and data minimization for the form itself.
How Much Do CAPTCHA Alternatives Cost?
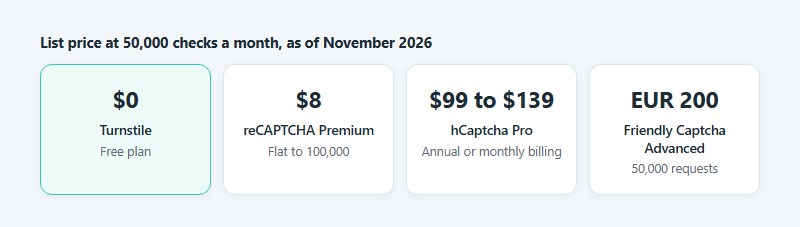
Turnstile and the open-source widgets cost nothing to run. reCAPTCHA is free to 10,000 assessments a month, then $8 flat up to 100,000, while hCaptcha Pro starts at $99 a month and Friendly Captcha at EUR 9. Figures are as of November 2026, taken from each vendor’s own documentation.
| Service | Free tier | Paid entry | Basis |
|---|---|---|---|
| reCAPTCHA (Essentials, Premium) | 10,000 assessments a month | $8 flat to 100,000, then $1 per 1,000 | Google Cloud billing documentation |
| Cloudflare Turnstile | Unlimited challenges, 20 widgets | Enterprise, by quote | Cloudflare plans page |
| hCaptcha | Basic plan, $0 (cap disputed) | Pro $99 a month billed annually or $139 monthly, 100,000 evaluations, then $0.99 per 1,000 | hCaptcha pricing page |
| Friendly Captcha | 1,000 requests, non-commercial | EUR 9 (1,000), EUR 39 (5,000), EUR 200 (50,000) | Friendly Captcha sign-up page |
| ALTCHA, Cap, mCaptcha | Free, self-hosted | Hosting and upkeep | Project documentation |
The table hides some disagreement between sources.
- Google’s billing documentation says the 10,000 free reCAPTCHA assessments aggregate across all accounts and sites in an organization. Several tutorials say per project.
- Secondary sources date the drop from 1 million to 10,000 free assessments to April 2024, early 2025 and April 2026. Google’s documentation states the current rule without a date.
- Cloudflare’s plans page (updated August 2026) says unlimited challenges and 20 widgets, while older material, including Piano’s integration docs, says 10 widgets and 1 million siteverify requests a month.
- Reviews put hCaptcha’s free-tier cap at 100,000 requests in one place and 10,000 in another, and the current pricing page lists no cap.
With no billing account attached, reCAPTCHA returns an error after the 10,000th assessment of the month (a 429 quota error, per Google), so a busy form can stop working mid-month.
Price per check and price per bypass sit closer than most buyers expect. Google charges $1 per 1,000 assessments above 100,000, and F5 Labs found human solver services selling solved reCAPTCHAs at $2.99 per 1,000.
Proof-of-work changes that arithmetic by charging compute instead of money, which is where the self-hosted options earn their place.
At 50,000 checks a month the list prices come to $8 for reCAPTCHA Premium, $0 for Turnstile, $99 to $139 for hCaptcha Pro and EUR 200 for Friendly Captcha Advanced. The privacy and EU-hosting premium is real, and so is the question of whether a given form needs it.
When CAPTCHA Alternatives Fail
Every method here breaks somewhere, and the breaks are fairly specific.
Solver services and CAPTCHA farms
The bot hands the challenge to a solver service, a human or a model earns a token, and the bot submits that token to your form (F5 Labs). The token is genuine, so your server has nothing to inspect.
AIMultiple’s survey of solver vendors quotes $2 to $3 per 1,000 for reCAPTCHA v2 and hCaptcha at one vendor, and $5 to $10 per 1,000 for reCAPTCHA v3, Enterprise, FunCaptcha and Turnstile.
Turnstile and score-based checks are on the price lists too. Nothing is unbeatable, so the goal is to make each fraud attempt cost more than it returns.
Headless browsers and human spammers
A headless browser runs your widget like any other visitor.
Proof-of-work widgets execute in the browser, so a script that can run JavaScript can compute the proof. An open-source solver published on docs.rs lists ALTCHA, Friendly Captcha, mCaptcha and Cap as supported targets, though its own documentation says live solve rates have not been benchmarked.
Scoring has a data problem too. Google’s documentation says reCAPTCHA learns from real traffic on your site, and its LOW_CONFIDENCE_SCORE reason code means too little traffic arrived to produce a quality risk analysis.
Verify the action name and hostname in every response, and treat tokens as single-use and short-lived. Per-account rate limits go on top.
Where passkeys and tokens do not apply
Passkeys leave a back door. Device-bound passkeys are lost with the device, and many consumer apps keep a fallback such as an email one-time code for devices without passkeys and for recovery (MojoAuth’s passkey glossary).
Bots go where friction is lowest, so that fallback needs its own rate limits and scoring.
Full platforms such as DataDome and Cloudflare Bot Management take over when the lighter layers run out. Cloudflare’s product page notes that Turnstile Enterprise is included with a Bot Management for Enterprise subscription.
Escalation makes sense once credential stuffing hits the login form or fake-account waves get past every widget. Fraud showing up at checkout is the other trigger.
Which Alternative Fits Which Form?
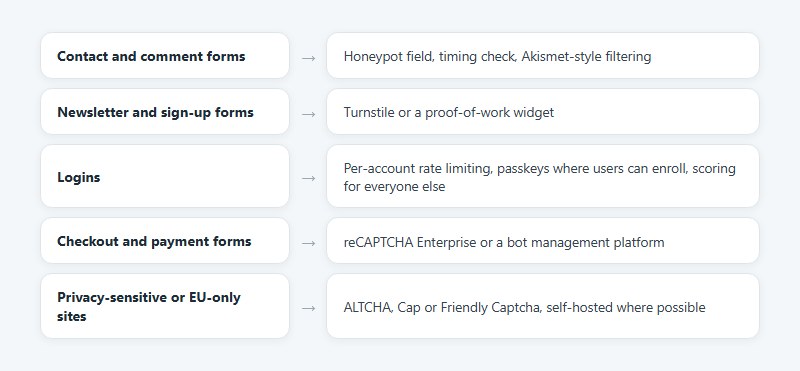
The rule I’d follow is to use the cheapest layer that still costs the attacker more than the form is worth to them.
- Contact and comment forms do fine with a honeypot field, a timing check and Akismet-style filtering.
- Newsletter and sign-up forms suit Turnstile or a proof-of-work widget.
- Logins get per-account rate limiting, passkeys where users can enroll, and scoring for everyone else.
- Checkout and payment forms call for reCAPTCHA Enterprise or a bot management platform.
- Privacy-sensitive or EU-only sites should look at ALTCHA, Cap or Friendly Captcha, self-hosted where possible.
WordPress sites can add Turnstile or Friendly Captcha through plugins, and a separate guide on how to stop spam from WordPress contact forms goes deeper on that platform. IvyForms, a WordPress form plugin, has Turnstile, hCaptcha and reCAPTCHA fields you can add from the form builder.
Each layer fails differently, so a honeypot, a widget and rate limits together cover more ground than any one of them alone.
How to Replace reCAPTCHA Step by Step
Anything with real traffic deserves a staged rollout.
- List every form and endpoint that loads the reCAPTCHA script, along with the action each one protects.
- Choose a replacement per form, based on what an attacker gains from it, instead of one tool for the whole site.
- Create the new provider’s site key and secret key. For Turnstile that also means picking a widget mode.
- Replace the client widget. Remove the recaptcha api.js script tags, add the new widget, and confirm its token posts with the form (g-recaptcha-response before, cf-turnstile-response for Turnstile).
- Change the server check. Turnstile uses a Siteverify endpoint on challenges.cloudflare.com, ALTCHA verifies locally with its server libraries and makes no external call, and providers with reCAPTCHA-shaped endpoints turn this into a URL swap. Google’s current documentation reserves its siteverify endpoint for legacy integrations and points new ones to CreateAssessment, so search your code for both.
- Handle token lifetime. Google tokens last two minutes and Turnstile tokens 300 seconds, and both are single use, so a stale or replayed token fails with timeout-or-duplicate. Refresh the token on forms that sit open.
- Run both providers in parallel. Log the new verdict without blocking on it, compare it with reCAPTCHA’s, and adjust thresholds before enforcing.
- Cut over. Delete the Google keys from your environment variables, remove the script, and update the cookie banner and privacy notice to match what now loads.
Skipping server validation is the usual mistake, since Cloudflare’s documentation warns that without it an attacker can submit any string to your endpoint. Leaving the secret key in client code is another.
Cloudflare provides test secret keys that always pass or always fail, which makes staging checks predictable.
CAPTCHA Alternatives FAQ
How is a CAPTCHA different from bot detection?
Bot detection is the wider practice of scoring traffic from signals such as IP reputation, behavior and device data. A CAPTCHA is one test a visitor has to pass inside that picture.
Modern services blur the line by running detection first and asking for interaction only when the score is poor.
Does Cloudflare Turnstile require Cloudflare DNS?
No. Cloudflare’s launch announcement says any developer can use Turnstile whether or not they are a Cloudflare customer.
You still create the widget in a Cloudflare account, which issues the site key and secret key.
Do verification widgets affect page speed?
Yes, slightly, and the size varies by vendor. ALTCHA’s README lists Turnstile at 85+ kB, hCaptcha at 250+ kB and reCAPTCHA at 300+ kB, against 34 kB gzipped for its own widget.
Cap’s comparison page puts hCaptcha above 600 KB, so vendor figures disagree. Measure the widget on your own pages before choosing.
Is email verification a CAPTCHA alternative?
Partly. Email verification proves an address is reachable, which stops throwaway fakes, but a script that can read an inbox follows the link too.
Treat it as a second layer behind a scoring or proof-of-work check, not as the first line of defense.
Monitoring CAPTCHA Alternatives After the Switch
CAPTCHA alternatives need monitoring after launch, because bypass tooling adapts and a valid token says nothing about who submitted it. Compare block rate and completed submissions per form against the pre-switch baseline. On WordPress, the entries table of a form plugin can show each submission with its date.
Spam that reaches the inbox comes first, since it is the only ground truth. Completed submissions per form come next, then the gap between challenge time and submission time. Google’s and Cloudflare’s siteverify responses both carry challenge_ts, and clusters of near-identical gaps deserve a closer look as possible solver-fed traffic.
Tightening a threshold trades missed bots for rejected visitors, so change one layer at a time. A guide to tracking form submissions in Google Analytics shows how to catch a drop in completions early.
This advice holds as of November 2026. It changes if Private Access Tokens or Privacy Pass redemption extend beyond Apple devices and make token verification a first layer.